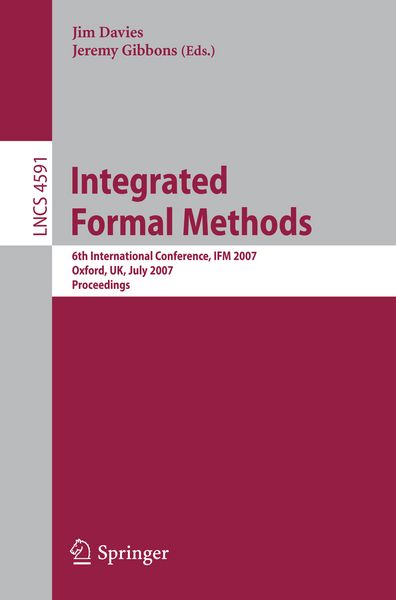
Integrated Formal Methods 6th International Conference, IFM 2007, Oxford, UK, July 2-5, 2007, Proceedings
-
- Englisch ausgewählt
95,99 €
UVP
106,99 €
inkl. gesetzl. MwSt.,
Beschreibung
Produktdetails
Einband
Taschenbuch
Erscheinungsdatum
22.06.2007
Abbildungen
IX, 662 p.
Herausgeber
Jim Davies + weitereVerlag
Springer BerlinSeitenzahl
662
Maße (L/B/H)
23,5/15,5/3,6 cm
Gewicht
1001 g
Auflage
2007
Sprache
Englisch
ISBN
978-3-540-73209-9
Verifying Temporal Properties of CommUnity Designs.- Precise Scenarios - A Customer-Friendly Foundation for Formal Specifications.- Automated Verification of Security Policies in Mobile Code.- Slicing Concurrent Real-Time System Specifications for Verification.- Slotted-Circus.- Bug Hunting with False Negatives.- Behavioural Specifications from Class Models.- Inheriting Laws for Processes with States.- Probabilistic Timed Behavior Trees.- Guiding the Correction of Parameterized Specifications.- Proving Linearizability Via Non-atomic Refinement.- Lifting General Correctness into Partial Correctness is ok.- Verifying CSP-OZ-DC Specifications with Complex Data Types and Timing Parameters.- Modelling and Verification of the LMAC Protocol for Wireless Sensor Networks.- Finding State Solutions to Temporal Logic Queries.- Qualitative Probabilistic Modelling in Event-B.- Verifying Smart Card Applications: An ASM Approach.- Verification of Probabilistic Properties in HOL Using the Cumulative Distribution Function.- UTP Semantics for Web Services.- Combining Mobility with State.- Algebraic Approaches to Formal Analysis of the Mondex Electronic Purse System.- Capturing Conflict and Confusion in CSP.- A Stepwise Development Process for Reasoning About the Reliability of Real-Time Systems.- Decomposing Integrated Specifications for Verification.- Validating Z Specifications Using the ProB Animator and Model Checker.- Verification of Multi-agent Negotiations Using the Alloy Analyzer.- Integrated Static Analysis for Linux Device Driver Verification.- Integrating Verification, Testing, and Learning for Cryptographic Protocols.- Translating FSP into LOTOS and Networks of Automata.- Common Semantics for Use Cases and Task Models.- Unifying Theories of Objects.- Non-interferenceProperties for Data-Type Reduction of Communicating Systems.- Co-simulation of Distributed Embedded Real-Time Control Systems.
Ein neues Kapitel für Ihre Bücher
Ein neues Kapitel für Ihre Bücher
Schenken Sie Ihren alten Schätzen ein zweites Leben und erhalten Sie dafür eine Thalia Geschenkkarte.
Noch keine Bewertungen vorhanden
Verfassen Sie die erste Bewertung zu diesem Artikel
Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.
Kurze Frage zu unserer Seite
Vielen Dank für Ihr Feedback
Wir nutzen Ihr Feedback, um unsere Produktseiten zu verbessern. Bitte haben Sie Verständnis, dass wir Ihnen keine Rückmeldung geben können. Falls Sie Kontakt mit uns aufnehmen möchten, können Sie sich aber gerne an unseren Kund*innenservice wenden.
zum Kundenservice