KI-Beratung Beta

  • Produktbild: Recent Advances in Intrusion Detection
  • Produktbild: Recent Advances in Intrusion Detection
Band 5758

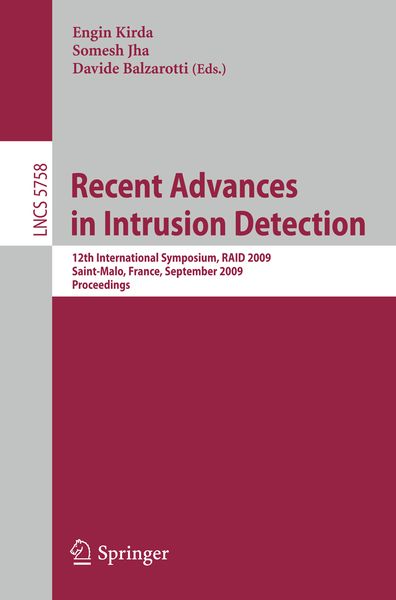
Recent Advances in Intrusion Detection 12th International Symposium, RAID 2009, Saint-Malo, France, September 23-25, 2009, Proceedings

49,99 €

inkl. gesetzl. MwSt., Versandkostenfrei


Beschreibung

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

11.09.2009

Abbildungen

XIII, 384 p.

Herausgeber

Engin Kirda + weitere

Verlag

Springer Berlin

Seitenzahl

384

Maße (L/B/H)

23,5/15,5/2,2 cm

Gewicht

604 g

Auflage

2009

Sprache

Englisch

ISBN

978-3-642-04341-3

Beschreibung

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

11.09.2009

Abbildungen

XIII, 384 p.

Herausgeber

Verlag

Springer Berlin

Seitenzahl

384

Maße (L/B/H)

23,5/15,5/2,2 cm

Gewicht

604 g

Auflage

2009

Sprache

Englisch

ISBN

978-3-642-04341-3

Herstelleradresse

Springer-Verlag KG
Sachsenplatz 4-6
1201 Wien
AT

Email: ProductSafety@springernature.com

Ein neues Kapitel für Ihre Bücher

Ein neues Kapitel für Ihre Bücher

Schenken Sie Ihren alten Schätzen ein zweites Leben und erhalten Sie dafür eine Thalia Geschenkkarte.

Jetzt verkaufen
Jetzt verkaufen

Noch keine Bewertungen vorhanden

Verfassen Sie die erste Bewertung zu diesem Artikel

Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.

Kundinnen und Kunden meinen

Bewertungen (0)

  • Produktbild: Recent Advances in Intrusion Detection
  • Produktbild: Recent Advances in Intrusion Detection
  • Recent Advances in Intrusion Detection Anomaly and Specification-Based Approaches.- Panacea: Automating Attack Classification for Anomaly-Based Network Intrusion Detection Systems.- Protecting a Moving Target: Addressing Web Application Concept Drift.- Adaptive Anomaly Detection via Self-calibration and Dynamic Updating.- Runtime Monitoring and Dynamic Reconfiguration for Intrusion Detection Systems.- Malware Detection and Prevention (I).- Malware Behavioral Detection by Attribute-Automata Using Abstraction from Platform and Language.- Automatic Generation of String Signatures for Malware Detection.- PE-Miner: Mining Structural Information to Detect Malicious Executables in Realtime.- Network and Host Intrusion Detection and Prevention.- Automatically Adapting a Trained Anomaly Detector to Software Patches.- Towards Generating High Coverage Vulnerability-Based Signatures with Protocol-Level Constraint-Guided Exploration.- Automated Behavioral Fingerprinting.- Intrusion Detection for Mobile Devices.- SMS-Watchdog: Profiling Social Behaviors of SMS Users for Anomaly Detection.- Keystroke-Based User Identification on Smart Phones.- VirusMeter: Preventing Your Cellphone from Spies.- High-Performance Intrusion Detection.- Regular Expression Matching on Graphics Hardware for Intrusion Detection.- Multi-byte Regular Expression Matching with Speculation.- Malware Detection and Prevention (II).- Toward Revealing Kernel Malware Behavior in Virtual Execution Environments.- Exploiting Temporal Persistence to Detect Covert Botnet Channels.- Posters.- An Experimental Study on Instance Selection Schemes for Efficient Network Anomaly Detection.- Automatic Software Instrumentation for the Detection of Non-control-data Attacks.- BLADE: Slashing the Invisible Channel of Drive-by DownloadMalware.- CERN Investigation of Network Behaviour and Anomaly Detection.- Blare Tools: A Policy-Based Intrusion Detection System Automatically Set by the Security Policy.- Detection, Alert and Response to Malicious Behavior in Mobile Devices: Knowledge-Based Approach.- Autonomic Intrusion Detection System.- ALICE@home: Distributed Framework for Detecting Malicious Sites.- Packet Space Analysis of Intrusion Detection Signatures.- Traffic Behaviour Characterization Using NetMate.- On the Inefficient Use of Entropy for Anomaly Detection.- Browser-Based Intrusion Prevention System.- Using Formal Grammar and Genetic Operators to Evolve Malware.- Method for Detecting Unknown Malicious Executables.- Brave New World: Pervasive Insecurity of Embedded Network Devices.- DAEDALUS: Novel Application of Large-Scale Darknet Monitoring for Practical Protection of Live Networks.